In brief
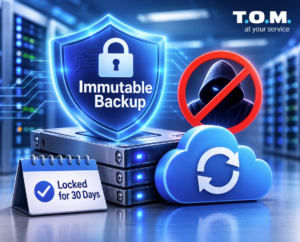
An immutable backup is a backup copy kept in storage that prevents changes and deletion for a defined period. Depending on the product and the lock mode, even the system administrator, and therefore an attacker who has stolen the administrator’s password, cannot modify or delete it until the period ends.
Intended for: small and midsize businesses and IT staff. Current as of 11/2026
| Risk classification: 🟢 Green – safe: Understanding the concept and planning the lock period.
🟡 Yellow – for IT staff: Governance-mode locking in the cloud (can be overridden) and snapshot locking on a NAS (network-attached storage), which usually cannot be overridden until the period ends. 🔴 Red – only after consulting an expert: Compliance mode and a WORM folder, which are usually irreversible. This article does not include detailed implementation instructions. |
What it is, in plain language
A regular backup is a file that anyone with sufficient permissions can delete. Ransomware attackers often try to do exactly that before encrypting data, so there is no way to recover without paying. With an immutable backup, the copy is usually stored under a WORM model (write once, read many).
Some products, such as Amazon S3 Object Lock and Acronis cloud storage, offer two modes. In Governance mode, an administrator with special permissions can remove or shorten the lock. In Compliance mode, no one can, not even an administrator, and the choice cannot be reversed; in S3, only deleting the entire AWS account bypasses it.
Immutable storage is not a regular snapshot, which an administrator can delete, and it is not an offline (disconnected) copy.
Why it matters
Because backups are a primary target. In a 2024 survey commissioned by Sophos, covering 2,974 IT professionals in 14 countries at organizations with 100 to 5,000 employees that had been hit by ransomware, 94% reported that attackers tried to compromise their backups, and 57% of those attempts succeeded. Organizations whose backups were compromised were almost twice as likely to pay a ransom to recover encrypted data (67% versus 36% among those whose backups were not compromised), and only 26% of them fully recovered within a week (versus 46%). These are correlations, not causation.
Because Acronis data shows locking is still uncommon. According to an analysis by the Acronis Threat Research Unit of data from its own platform (not a representative survey), of about 846,000 accounts with a lock configured, roughly 30% had an active lock, and about 98.6% of backup volume was not locked (Acronis’s calculation).
Because it is part of a broader plan. In our article Business Continuity and Cloud DR, a locked copy is one of the plan’s five components.
| Scenario | Is immutable backup a fit? |
|---|---|
| An organization that backs up to the cloud or a NAS and wants ransomware protection | Usually yes |
| Data subject to retention or deletion requirements | Depends – after reviewing the requirements |
| Shortening recovery time | No – we wrote about recovery time here |
| Data that has already been corrupted or encrypted | No – a corrupted copy gets locked too |
| A substitute for restore testing | No – a locked copy that has not been tested is still an assumption |
How to get there
The examples are for illustration only; other products may offer similar locking.
1. Cloud storage with built-in locking. According to Acronis documentation, since September 2024 its hosted storage has Governance mode enabled by default with a 14-day period (verify with the vendor). Support is limited to certain agent versions and the TIBX format, and the setting applies to an existing archive only after a new backup is created in it.
2. Locking on a local NAS device. On Synology (DSM 7.2, Btrfs, supported models), a snapshot can be locked for up to 30 days, and according to the vendor’s blog, even a compromised administrator cannot delete it. For longer retention there is a WriteOnce folder, which cannot be converted back to a regular one: in Enterprise mode an authorized administrator can delete it, and in Compliance mode it is deleted only after all the files in it have reached the end of their retention period. QNAP also supports WORM, according to its documentation for QuTS hero (one of its operating systems), but in Compliance mode an administrator can delete the folder by removing the entire storage pool.
The recommended combination: a fast local copy and a protected off-site copy.
What to check before you start
Check what is already active: whether locking is enabled in the cloud, in which mode and for how many days, and whether the NAS model supports it. Estimate capacity based on the backup type, change rate, compression, and lock period.
How to roll back
In Governance mode you can usually turn off the lock or shorten it, but what happens to backups that were already locked depends on the product. With a locked snapshot or Compliance mode, there is usually no way to cancel or shorten the lock until the period ends, and you cannot go back to Governance or convert a folder back to a regular one. So start with Governance and short periods, and move to Compliance only after checking capacity and cost.
Risks and warnings
Locked capacity and cost. The capacity is held until the period ends, and according to Acronis, in the cloud it is also billed. Monitor capacity and cost.
Locking is not cleanup. An attacker may have been in the network for an unknown length of time, and the locked copies may already contain traces of the intrusion. Restore from a clean point, after scanning and resetting passwords.
Governance is only as strong as the administrator account. Use separate accounts for the backup system, two-factor authentication, and least-privilege permissions. Locking does not protect against fire or theft of a NAS located at the production site.
| T.O.M recommendation: In our view, an immutable backup copy is an essential component of a backup plan, particularly for core systems, and not an optional upgrade; its scope should be set according to risk. Check whether your cloud service already locks backups and for how many days, and if you have a supported NAS, add a short snapshot lock on a single folder. In the cloud, 14 to 30 days is a reasonable starting point (the range Acronis generally recommends for weekly full backups of important workloads), provided that you detect a failure or breach within the period. Periodically test a restore from the locked copy, including confirming that the business service works. Not sure whether your backups are protected from an attacker with admin rights? We would be glad to review it with you. |
Sources
• Sophos, The impact of compromised backups on ransomware outcomes, 2024 survey
• Sophos, The impact of compromised backups on ransomware outcomes, White Paper, 2024
• Acronis Cyber Protect 16 documentation: Immutable storage
• Acronis Cyber Protect 16 documentation: Enabling immutable storage
• Synology, WriteOnce (WORM) White Paper, DSM 7.2
• Synology, When Only Immutable Backups Survive, 7.7.2026
• Synology, Which Synology NAS models support WriteOnce and immutable snapshots
• QNAP, Immutable storage, QuTS hero
• QNAP, What is the difference between Enterprise and Compliance WORM?
• Amazon S3, Locking objects with Object Lock
• T.O.M, Business Continuity and Cloud DR: How to Prepare Properly, 26.10.2026
• T.O.M, An RTO Target on Paper vs. Recovery Speed in Reality: Why You Have to Measure, 8.9.2026
DisclaimerThe information in this article is provided for educational and general informational purposes only, based on public sources and current as of the time of writing. It does not constitute professional advice, a recommendation to act, or a substitute for an individual assessment of your environment. Systems, versions, network equipment, and organizational policies vary from one environment to another, so results may differ. Any change to system settings, particularly on servers and in production environments, is made at the sole responsibility of the person carrying it out, after documenting the current state, taking a backup, within a maintenance window, and with the approval of an authorized IT professional. T.O.M at your service Ltd will not be liable for any direct or indirect damage, data loss, or downtime resulting from applying this information. If in doubt, consult us before proceeding. |
👈 To book a consultation directly in our calendar: Click here
📲 Want a weekly professional tip delivered straight to your phone?
Join our WhatsApp channel – one computing, cyber, or cloud tip a week, no spam, and your number is not visible to anyone:
👈 Join with one click: Link
© T.O.M at your service Ltd | The Experts in Creating Peace of Mind | tom-comp.com